Threat modelling per service
STRIDE workshops on the components that matter, with findings tracked to closure.
Security that engineers adopt, not security that engineers route around.
Controls that slow delivery get bypassed, and a bypassed control is worse than no control because it creates false confidence. We embed security into the paths developers already use — pre-commit hooks, pipeline gates, paved-road templates — so the secure way is also the fastest way.
On the compliance side we build the evidence machinery, not just the policy documents. Automated control evidence, quarterly access reviews and a live risk register mean audit season stops being a two-month fire drill.
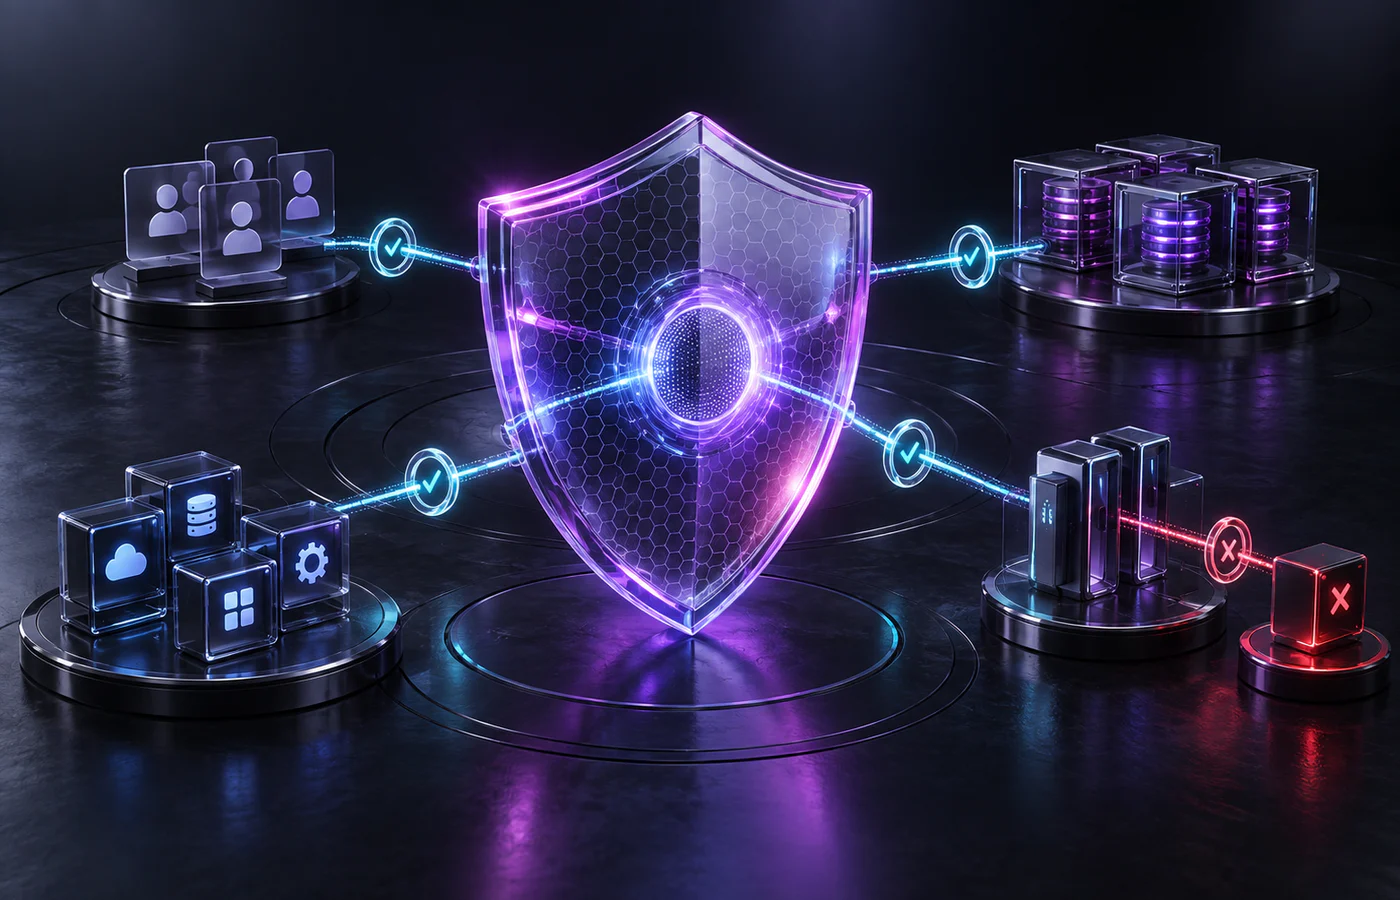
And what we do differently so they do not.
STRIDE workshops on the components that matter, with findings tracked to closure.
SAST, DAST, dependency and secret scanning wired into the pipeline with sane thresholds.
Least-privilege IAM, workload identity, short-lived credentials and full session audit.
Control mapping, automated evidence collection and a maintained risk register.
Yes. A typical Type I readiness programme runs twelve to sixteen weeks: gap assessment, control implementation, evidence automation, then a readiness review before your auditor engages. We work alongside your auditor; we do not act as one.
We do. Application, cloud configuration and internal network testing, delivered as a prioritised report with reproduction steps, plus a free retest of remediated findings within ninety days.
Bring us the messy version. We are more useful before the requirements document exists than after it has been signed off.